RBAC built-in
Four roles. Project routes gated. UI mirrors server.
Admin / Operator / Auditor / Viewer, scoped per project. The backend is authoritative, while the useCan(slug, action) hook mirrors the policy in the dashboard so users do not see controls their role cannot use. Admins own schedule-definition CRUD; operators can run commands and control existing schedules; auditors read the audit log and change nothing; viewers read ordinary project data. The audit log is open to auditors and admins only, so the people who review the record are not the people who produce it.
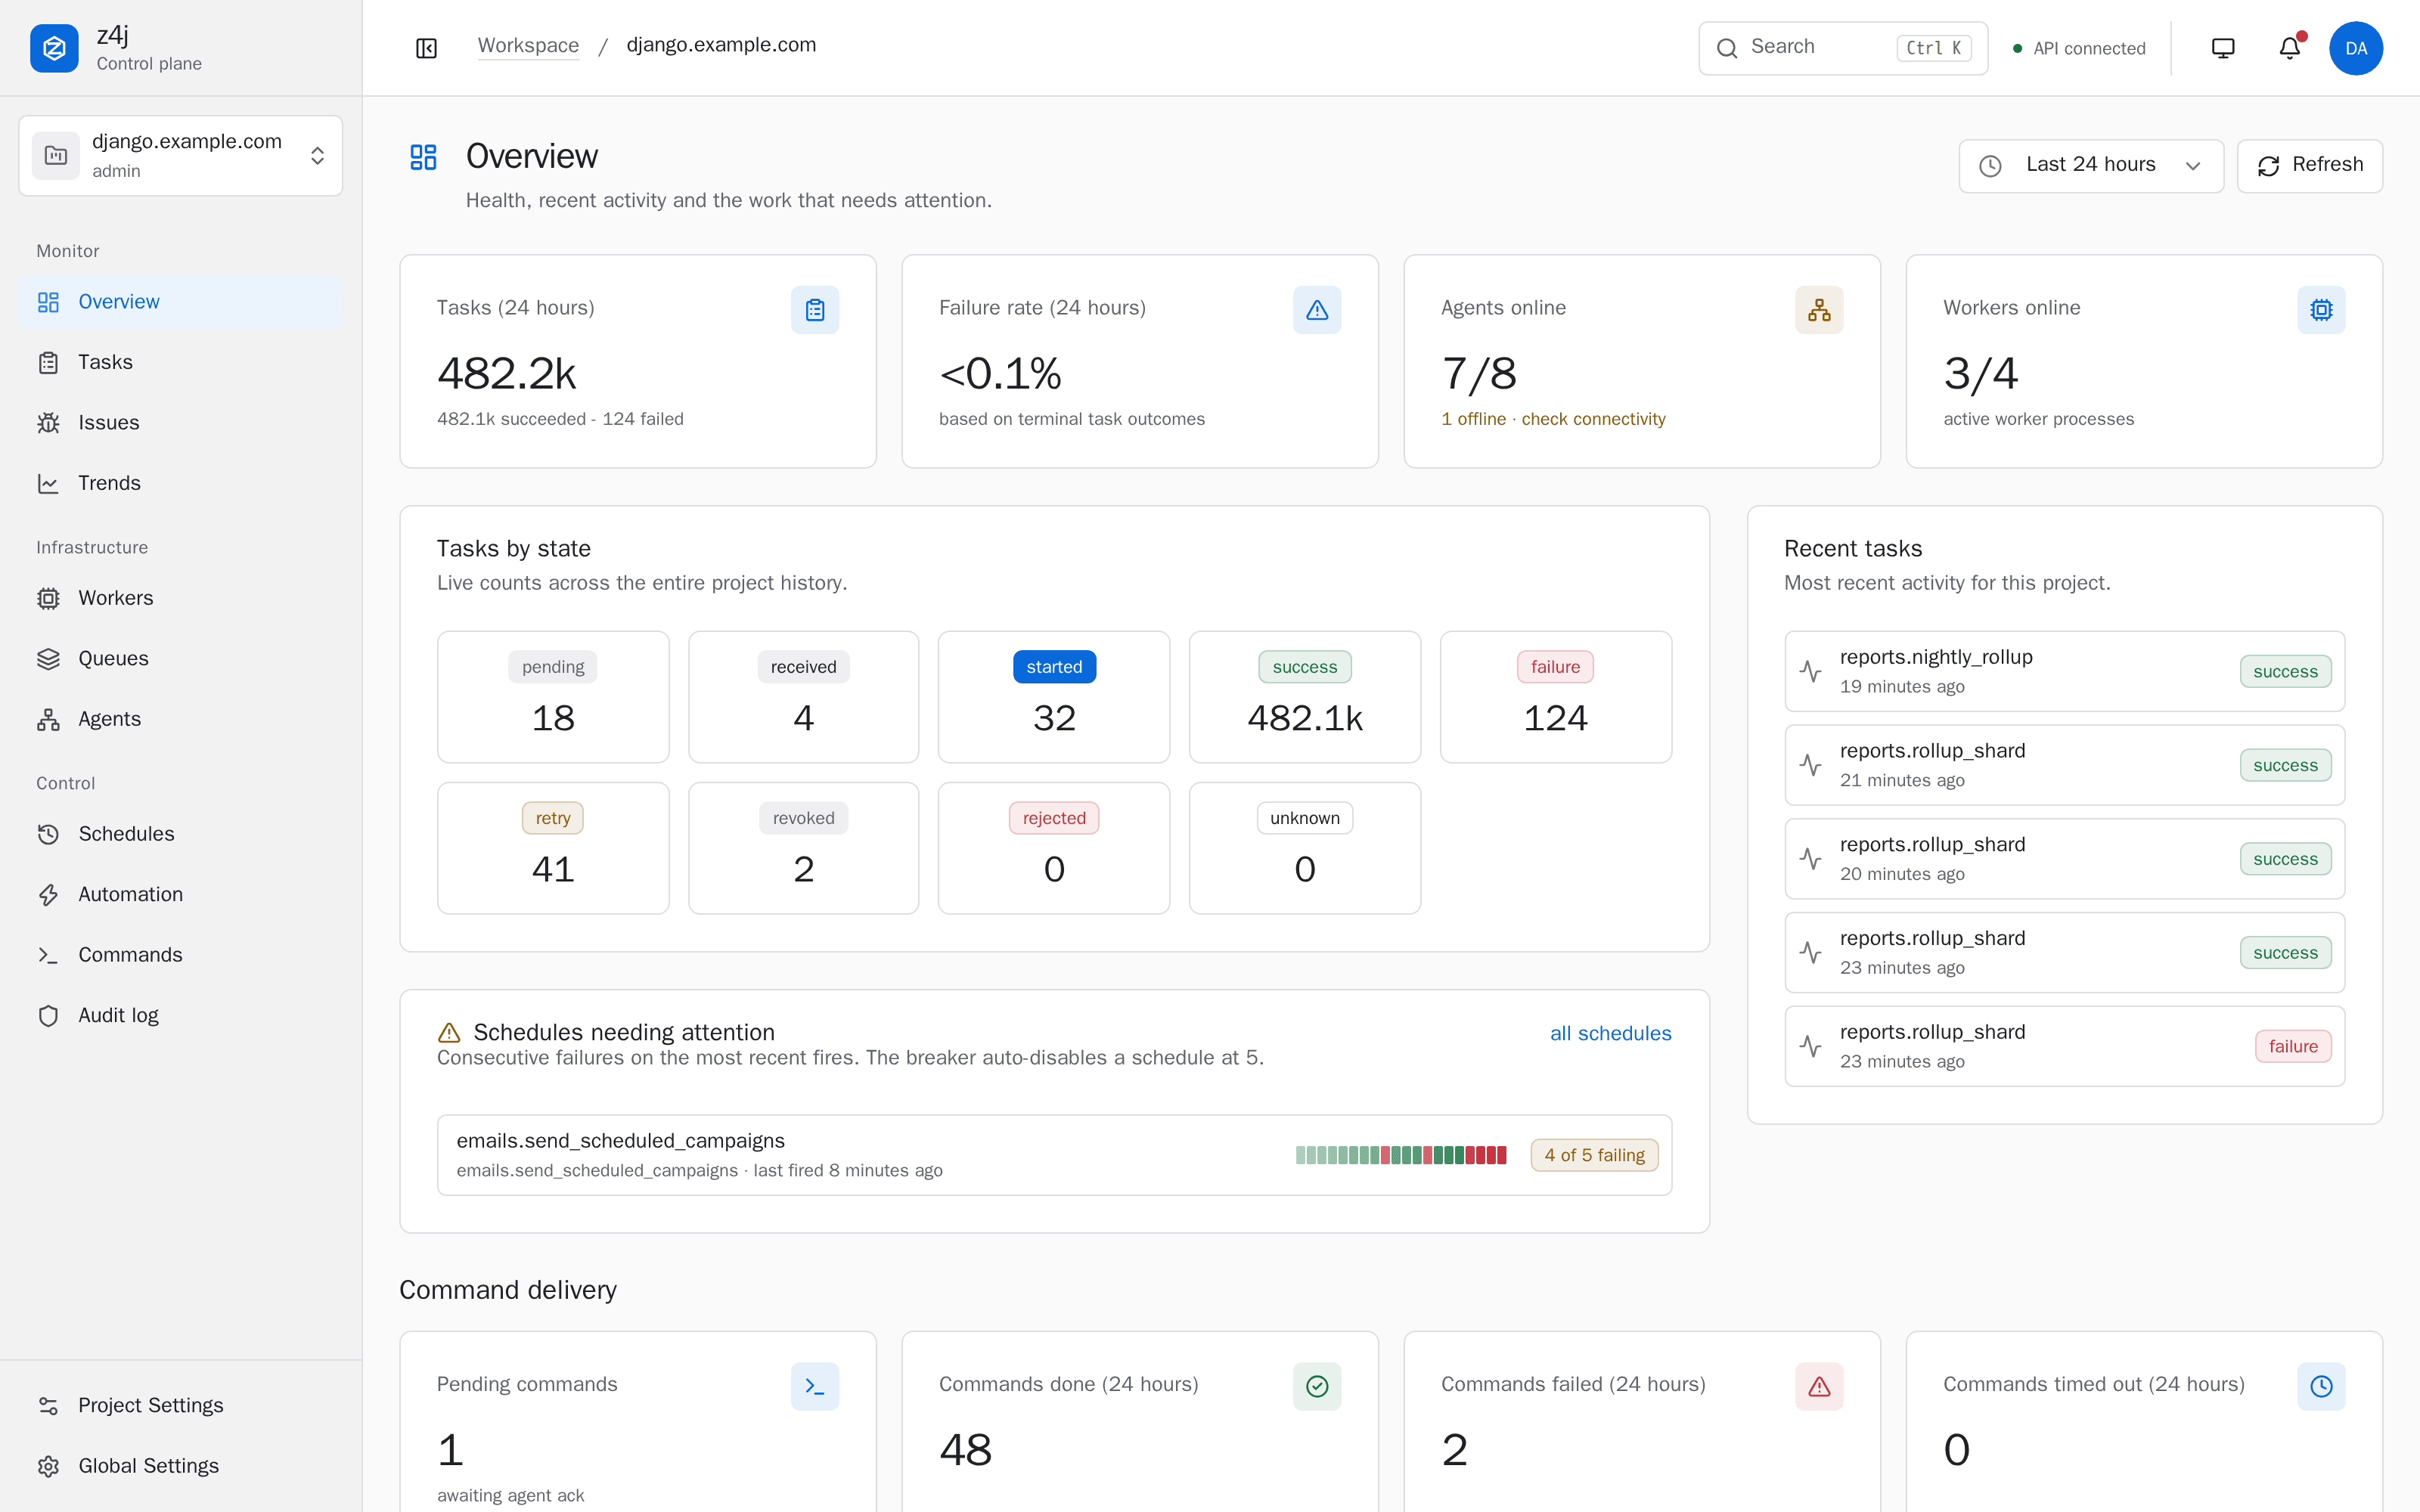
Mockup of the dashboard view for this feature. Live-reloading and themed to match your dashboard.
Ships with
- Backend as source of truth
- UI gates match server policy
- Debounced 'Permission denied' toast on any 403
- Per-project membership + last-admin protection
Related